NobleProg delivers specialized AI Security training in Leon, a hub of industrial and manufacturing excellence. Professionals in this region benefit from expert-led courses designed to enhance technical skills and drive innovation within the local business community.
Safeguard your AI infrastructure against emerging threats through practical, instructor-led AI Security training.
These live sessions equip you with the skills to protect machine learning models, neutralize adversarial attacks, and establish reliable, fault-tolerant AI frameworks.
Enrollment is available for online live instruction via remote desktop or in-person live sessions in Leon, both featuring interactive exercises and real-world application scenarios.
In-person sessions can be hosted at your facility in Leon or at a NobleProg corporate training center in Leon.
Also recognized as Secure AI, ML Security, or Adversarial Machine Learning.
NobleProg – Your Local Training Provider
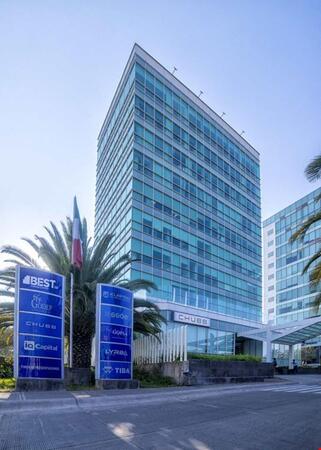
Leon - Torre San Mateo
Blvd. Campestre 2502 , Leòn, Mexico
Located in the Golden Zone of Leon Gto.
By public bus
León's public transport is the SIT/Optibús system. The city publishes current route and timetable information through its Mobility Department.
From León Centro: a practical option is to travel toward Terminal San Jerónimo, then continue toward the Campestre area.
Blvd. Campestre is served by local routes; for example, route L-02 runs along Boulevard Campestre and connects with Centro Histórico and San Jerónimo.
For the final part, you may need a short walk from the closest stop to No. 2502.
This advanced ISACA course in Leon empowers professionals to effectively govern and secure AI systems. It addresses risk assessment, secure design, and compliance, enabling leaders to align AI security with organizational objectives and significantly boost operational resilience.
This instructor-led, live training in Leon (online or onsite) is designed for beginner to intermediate IT professionals seeking to understand and implement AI TRiSM within their organizations.
Upon completing this training, participants will be able to:
Understand the core concepts and significance of AI trust, risk, and security management.
Identify and mitigate risks linked to AI systems.
Apply security best practices for AI.
Comprehend regulatory compliance and ethical considerations for AI.
Develop strategies for effective AI governance and management.
This instructor-led training in Leon focuses on governance, identity management, and red-teaming for agentic AI systems. Advanced practitioners will learn to design secure deployments, implement least-privilege access controls, and conduct adversarial testing to mitigate real-world threats in production environments.
This instructor-led, live training in Leon (online or onsite) is designed for intermediate-level AI and cybersecurity professionals who want to understand and address security vulnerabilities specific to AI models and systems, particularly in highly regulated industries such as finance, data governance, and consulting.
Upon completion of this training, participants will be able to:
Identify types of adversarial attacks targeting AI systems and learn defense strategies.
Apply model hardening techniques to secure machine learning pipelines.
Ensure data security and integrity in machine learning models.
Navigate regulatory compliance requirements related to AI security.
This instructor-led, live training in Leon (online or onsite) is aimed at advanced-level security professionals and ML specialists who wish to simulate attacks on AI systems, uncover vulnerabilities, and enhance the robustness of deployed AI models.
Upon completing this training, participants will be equipped to:
Simulate real-world threats to machine learning models.
Generate adversarial examples to test model robustness.
Assess the attack surface of AI APIs and pipelines.
Design red teaming strategies for AI deployment environments.
This instructor-led training in Leon empowers advanced professionals to secure TinyML pipelines on edge devices. You will learn to implement privacy-preserving techniques, harden models against adversarial threats, and apply best practices for secure data handling in constrained environments.
This instructor-led, live training in Leon (online or on-site) is aimed at intermediate-level engineers and security professionals who wish to secure AI models deployed at the edge against threats such as tampering, data leakage, adversarial inputs, and physical attacks.
By the end of this training, participants will be able to:
Identify and assess security risks in edge AI deployments.
Apply tamper resistance and encrypted inference techniques.
Harden edge-deployed models and secure data pipelines.
Implement threat mitigation strategies specific to embedded and constrained systems.
This instructor-led, live training in Leon (online or onsite) is aimed at advanced-level professionals who wish to implement and evaluate techniques such as federated learning, secure multiparty computation, homomorphic encryption, and differential privacy in real-world machine learning pipelines.
By the end of this training, participants will be able to:
Understand and compare key privacy-preserving techniques in ML.
Implement federated learning systems using open-source frameworks.
Apply differential privacy for safe data sharing and model training.
Use encryption and secure computation techniques to protect model inputs and outputs.
This instructor-led course in Leon empowers public sector IT professionals to excel in AI risk management and security. Learners will implement frameworks such as the NIST AI RMF, mitigate cybersecurity threats, and establish robust governance strategies to ensure secure AI deployment.
This instructor-led, live training in Leon (online or onsite) targets intermediate-level enterprise leaders who wish to understand how to govern and secure AI systems responsibly and in compliance with emerging global frameworks such as the EU AI Act, GDPR, ISO/IEC 42001, and the U.S. Executive Order on AI.
By the end of this training, participants will be able to:
Understand the legal, ethical, and regulatory risks of using AI across departments.
Interpret and apply major AI governance frameworks (EU AI Act, NIST AI RMF, ISO/IEC 42001).
Establish security, auditing, and oversight policies for AI deployment in the enterprise.
Develop procurement and usage guidelines for third-party and in-house AI systems.
This instructor-led, live training in Leon (online or in-person) targets AI developers, architects, and product managers at intermediate to advanced levels who wish to identify and mitigate risks associated with LLM-powered applications, including prompt injection, data leakage, and unfiltered output, while incorporating security controls like input validation, human-in-the-loop oversight, and output guardrails.
Upon completion of this training, participants will be able to:
Grasp the fundamental vulnerabilities inherent in LLM-based systems.
Implement secure design principles within LLM application architectures.
Utilize tools such as Guardrails AI and LangChain for validation, filtering, and ensuring safety.
Incorporate techniques like sandboxing, red teaming, and human-in-the-loop review into production-grade pipelines.
This instructor-led live training, available online or onsite, is aimed at intermediate-level machine learning and cybersecurity professionals who wish to understand and mitigate emerging threats against AI models, using both conceptual frameworks and hands-on defenses like robust training and differential privacy.
By the end of this training, participants will be able to:
Identify and classify AI-specific threats such as adversarial attacks, inversion, and poisoning.
Use tools like the Adversarial Robustness Toolbox (ART) to simulate attacks and test models.
Apply practical defenses including adversarial training, noise injection, and privacy-preserving techniques.
Design threat-aware model evaluation strategies in production environments.
This instructor-led, live training in Leon (online or onsite) is designed for beginner-level IT security, risk, and compliance professionals who want to grasp foundational AI security concepts, threat vectors, and global frameworks such as NIST AI RMF and ISO\/IEC 42001.
By the end of this training, participants will be able to:
Comprehend the distinct security risks introduced by AI systems.
Recognize threat vectors such as adversarial attacks, data poisoning, and model inversion.
Apply foundational governance models like the NIST AI Risk Management Framework.
Align AI usage with emerging standards, compliance guidelines, and ethical principles.
Based on the latest OWASP GenAI Security Project guidance, participants will learn to identify, assess, and mitigate AI-specific threats through hands-on exercises and real-world scenarios.
This course offers a practical introduction to securing modern AI-powered applications, APIs, copilots, and autonomous agents. Participants will learn how AI security diverges from traditional web security, explore common AI-specific threats such as prompt injection, RAG poisoning, and agent abuse, and understand how to protect AI systems using layered defenses including WAFs, AI gateways, API security, and guardrails. Through hands-on labs and real-world examples, students gain the skills to identify AI attack patterns, secure LLM-based applications, and deploy effective runtime defenses for production environments.
This course teaches software developers how to build AI-powered applications securely by design. Participants learn how to protect chatbots, copilots, RAG pipelines, and AI agents against AI-specific threats such as prompt injection, data poisoning, tool abuse, secret leakage, and insecure model output. The course covers secure prompt design, RAG security, least-privilege access, guardrails, and red-team testing, helping developers build AI features that are secure, reliable, and resilient in real-world environments.
This instructor-led, live training in Leon (online or onsite) is aimed at security engineers and compliance officers who wish to harden EXO deployments, control model access, and govern AI workloads running entirely on-premise.
This instructor-led, live training in Leon (online or onsite) is aimed at security and ML engineers who need to identify, test, and defend against attacks on ML models and LLM-powered applications.
Read more...
Last Updated:
Testimonials (3)
inventory and identifying the different risk exposures within AI
Gary Cook - Cybersecurity and Information Technology Risk Division
Course - Introduction to AI Trust, Risk, and Security Management (AI TRiSM)
I really enjoyed learning about AI attacks and the tools out there to begin practicing and actively using for security testing. I took a lot of knowledge away which I didn't have at the beginning and the course met what I hoped it would be. My favorite part shown from the training was Comet Browser and was amazed at what it could do. Definitely something will be looking into more. Overall it was a great course and enjoyed learning all OWASP GenAI Top 10.
Patrick Collins - Optum
Course - OWASP GenAI Security
The profesional knolage and the way how he presented it before us
Online AI Security training in Leon, Secure AI training courses in Leon, Weekend AI Security courses in Leon, Evening Secure AI training in Leon, Secure AI instructor-led in Leon, AI Security boot camp in Leon, Secure AI trainer in Leon, Secure AI private courses in Leon, AI Security instructor in Leon, Secure AI classes in Leon, Online Secure AI training in Leon, Evening AI Security courses in Leon, Secure AI on-site in Leon, AI Security coaching in Leon, Weekend Secure AI training in Leon, Secure AI one on one training in Leon, AI Security instructor-led in Leon